Uncompromising
Security.
Unmatched Scale.
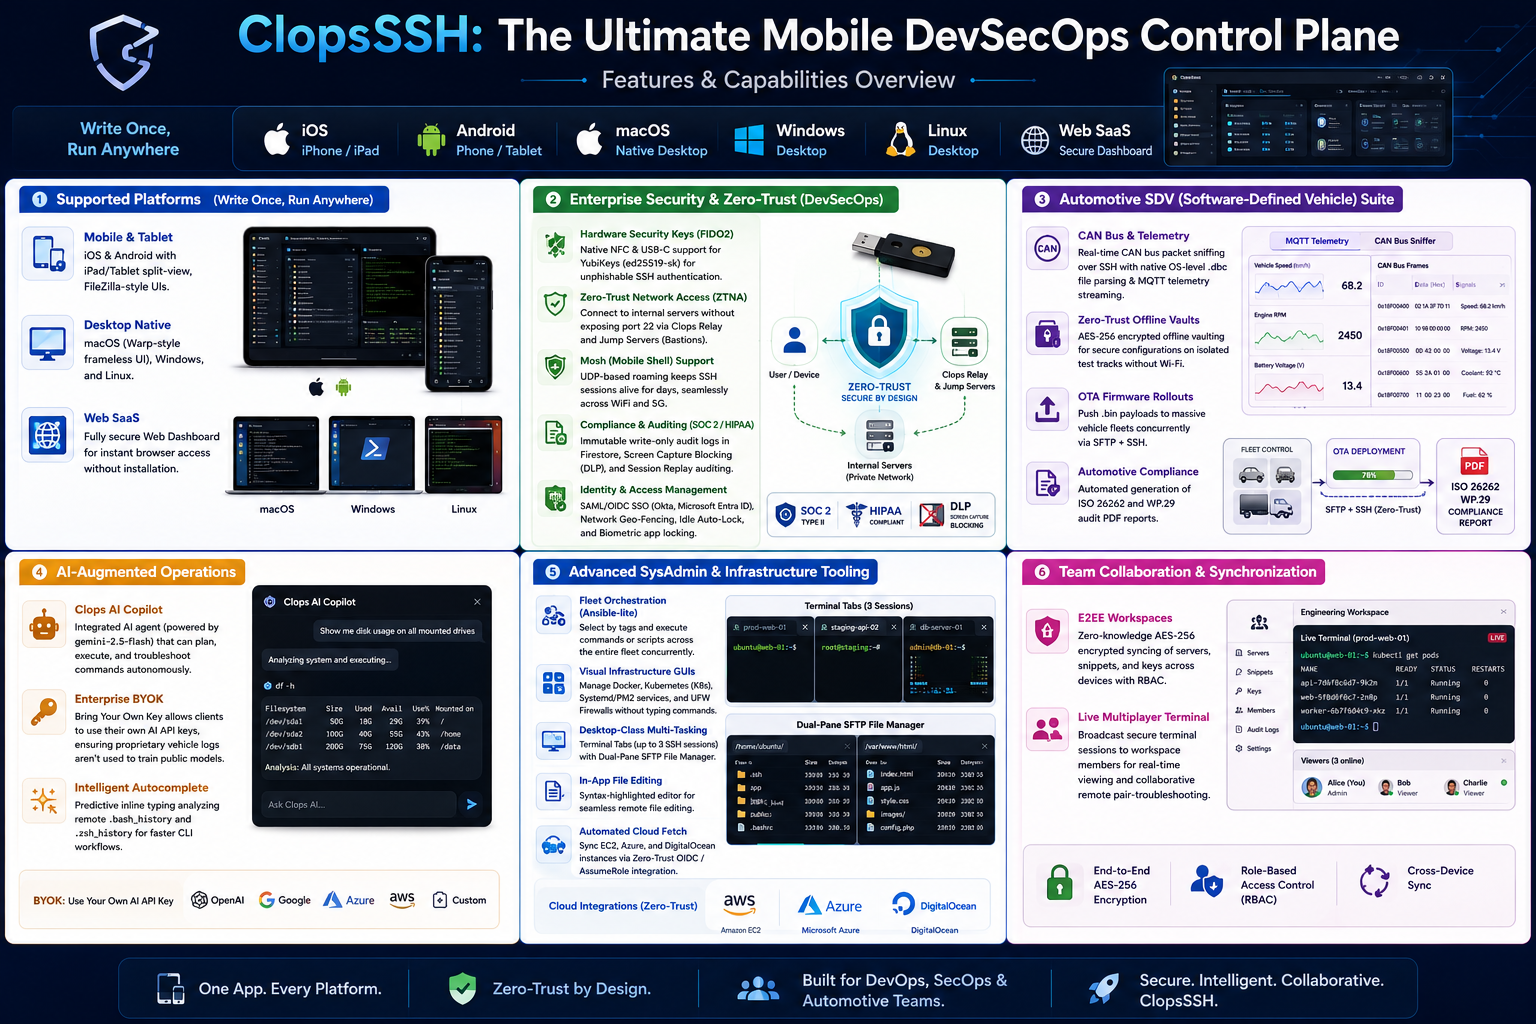
Deploy ClopsSSH across your entire IT organization with Zero-Trust architecture, FIDO2 hardware enforcement, and native Kubernetes orchestration.
Contact IT Solutions SalesCore Platform: SSH, SFTP & Terminal
The fastest, most secure terminal emulator and file browser built for modern development teams.
- GPU-Accelerated Terminal Emulator
- Visual SFTP File Browser & Editor
- Integrated Log Parsing & Highlighting
Identity & Access (PAM)
Enforce strict corporate access policies universally.
- SAML SSO (Okta, Entra ID)
- FIDO2 Hardware Keys (YubiKey)
- Network Geo-Fencing
E2EE Team Workspaces
Share infrastructure securely without ever exposing a private key to your team.
- AES-256 Cloud Sync
- Role-Based Access Control (RBAC)
- Live Session Auditing & Replay
Zero-Trust Cloud Fetch
Eliminate static SSH keys entirely. Automatically discover and connect to your cloud provider instances using ephemeral, short-lived certificates.
- AWS, Azure, & GCP Auto-Discovery
- HashiCorp Vault Integration
- Bastion / Jump Server Proxying
Enterprise Compliance
Meet the strictest regulatory requirements out-of-the-box.
- ISO 26262 & WP.29 Ready
- Zero-Knowledge Architecture
- MDM & AppConfig Overrides
Native Kubernetes & Docker
A completely visual cluster and container manager. Monitor nodes, manage pods, and stream logs without installing any external agents onto your infrastructure.
Hardware-Backed Identity (FIDO2)
Private key material never enters application storage. Authenticate via physical YubiKeys and FIDO2 tokens using native OpenSSH Security Key (SK) integration.
True Zero-Knowledge
The hardware security key performs the cryptographic signing operation. Private keys are never exposed to the OS or RAM.
Supported Protocols
sk-ssh-ed25519@openssh.com
sk-ecdsa-sha2-nistp256@openssh.com
Cross-Platform CTAP
Seamless USB, NFC, and Bluetooth hardware token support across macOS, Linux, Android, iOS, and iPadOS.
Zero Trust Network Access (ZTNA)
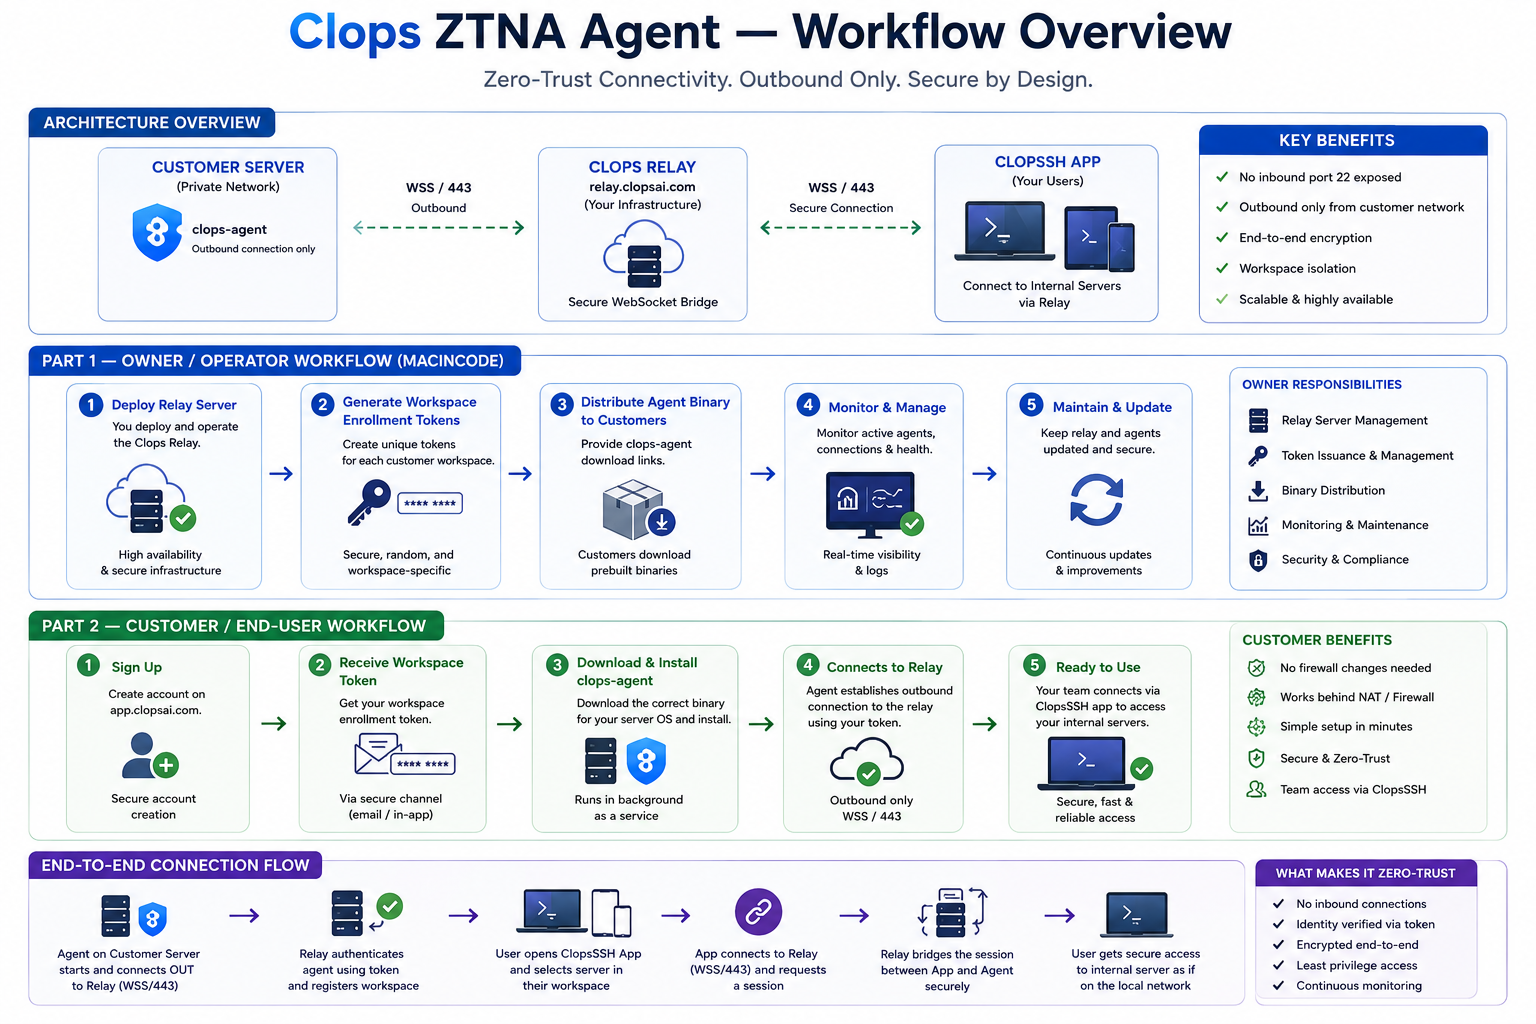
Connect to private servers behind corporate firewalls or NAT without VPNs or opening inbound ports. End-to-end encrypted SSH over WebSocket tunnels.
Clops App
Initiates SSH connection
Clops Relay
wss://relay.clopsai.com
Bridges TCP to WS
Private Server
Runs Clops Agent
No public IP
The B2B2C Growth Pipeline
How Clops SSH scales organically from individual developers to global enterprise deployments via Product-Led Growth.
1. Acquisition
Solo developers adopt Clops for personal use via public app stores.
2. Activation
Users experience the "Aha!" moment with beautiful UI and AI Copilot.
3. Expansion
Teams form organically via Domain Auto-Onboarding & E2EE sharing.
4. Enterprise Conversion
IT departments upgrade to unlock SAML SSO, MDM, and Audit Logs.
Compliance & Security Roadmap
Our commitment to providing enterprise-grade security and compliance for CISOs and IT administrators.
Phase 1: Foundation (Live)
Core security architecture and identity management.
- SAML SSO (Okta, Entra ID)
- MDM AppConfig Overrides
- Zero-Knowledge E2E Encryption
Phase 2: Access & Audit (Live)
Enterprise controls for session monitoring and restricted access.
- Session Replay Auditing (Firestore)
- Network Geo-Fencing (IP Allowlist)
- Ephemeral Vault SSH Certificates
Phase 3: Certification (Upcoming)
Third-party validation and centralized management.
- SOC 2 Type II Certification
- Centralized IT Admin Web Portal
- Third-Party Penetration Testing
Phase 4: Ecosystem (Future)
Deep integration into existing enterprise security stacks.
- SIEM Log Forwarding (Splunk/Datadog)
- Tailscale & Cloudflare Access Integration
- Autonomous AI Copilot Execution